

Check configurations.Assess risks.Stay in control.
SigXOS is developing a cybersecurity platform that checks configurations of network and security systems and assesses risks in the network and operational context. Changes are made only after your explicit approval.
PrototypeDevelopment status: working prototype for Cisco IOS/IOS-XE, tested with real devices.
Check run
Lab datarunning-configlines 11–15
- 11!
- 12enable secret 9 ••••••••••••
- 13no service password-encryption
- 14!
- 15ip ssh version 2
Password obfuscation enabled
- Evidence
- running-config, line 13
- Requirement
- CIS-oriented
- Measure
service password-encryption
- F004SSH version 2 enforcedPassed
- F005Telnet disabled on VTY linesPassed
- F007Access list on VTY linesDeviation
- Checks in the network and operational context
- AI explains and prepares measures
- Changes only after explicit approval
- Credentials and raw configurations stay with the customer
Solutions
Make security requirements testable
For companies with their own IT infrastructure and for IT service providers and system integrators who manage customer environments.
Security checks
Check configurations repeatably against defined security requirements instead of reviewing systems one by one.
Learn moreRisk assessment in context
Take system role, network environment and available dependencies into account and prioritise risks.
Learn moreTechnical evidence
Back up check results with the configuration line, requirement reference and time.
Learn moreMeasures under customer control
AI-assisted remediation proposals, technical review and execution only after explicit approval.
Learn more


Development status
Prototype for Cisco IOS/IOS-XE
The prototype has been tested with real devices and in simulation environments. We validate check quality, usefulness of the evidence and time savings in a paid pilot.
- Read-only collection via SSH, without software on the devices
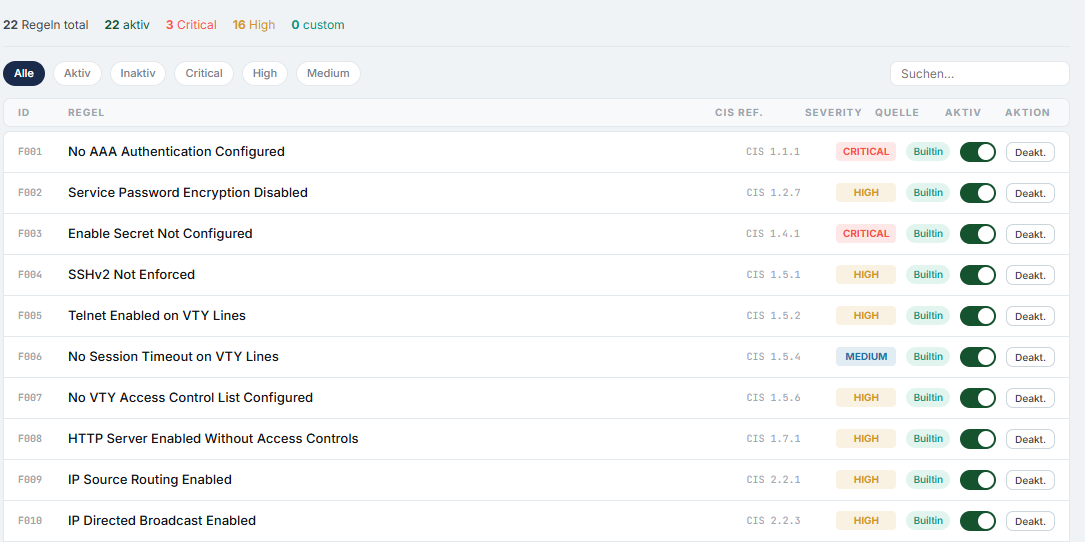
- CIS-oriented checks with reference and severity
- Findings with configuration evidence
- Inventory, audit trail and check report

Process
Controlled check and change process
Seven steps with clear responsibilities. Without a change order, the process ends with a report and recommended actions.
1Define scope
Define the check scope and access rights; capture systems and dependencies.
2Collect read-only
Collect configurations and inventory data strictly read-only.
3Assess in context
Assess configurations in the network and operational context, prioritise risks and propose measures.
4Review
Review measures, impact, tests and rollback procedures.
5Approve
Plan version, target systems and time window are approved by authorised customer owners or a service provider authorised to approve.
6Execute under control
Verify approval and prerequisites, back up the initial state and execute the approved plan.
7Verify and document
Check and document the result and operation. If required, start the prepared rollback procedure manually and check again.
In the prototype and the pilot, the process ends with a report and recommended actions; you implement changes yourself and SigXOS checks again. Controlled execution of approved changes (steps 4 to 7) is part of the target architecture. Process in detail

Evidence, not assumptions
Every statement about the security state should trace back to the actual configuration.
More about our approachScope
Technologies & platforms, security requirements & recommendations
Example selection. Platform support is extended based on customer demand, market demand and technical validation.
Technologies & platforms
- CiscoIOS / IOS-XEPrototype
- HPE Aruba NetworkingAOS-CXOn customer demand
- FortinetFortiOSOn customer demand
- Palo Alto NetworksPAN-OSOn customer demand
- HPE Juniper NetworkingJunos OSOn customer demand
- LinuxRed Hat Enterprise Linux, Ubuntu ServerPlanned
- MicrosoftEntra ID & Active Directory · check target: identityPlanned
Security requirements & recommendations
- CIS Benchmarks & ControlsHardening recommendationsPrototype
- NIS-2Planned
- BSIGPlanned
- DORAPlanned
- BSI IT-GrundschutzPlanned
- ISO/IEC 27001Planned
- PCI DSSPlanned
- NIST CSF 2.0Planned
- Internal policiesPlanned
Services
Start with a paid pilot
Together we find out whether SigXOS delivers the expected value in your environment.

Paid pilot
Four to six weeks, up to about 25 devices, with read-only collection in your environment.
Learn moreSet-up and review
Joint review of the check results and measurement of check quality, usefulness of the evidence and time savings.
Learn morePartner model
For IT service providers and system integrators who manage customer environments.
PlannedLearn more
Frequently asked questions
What is SigXOS?
SigXOS is developing a cybersecurity platform that checks configurations of network and security systems against defined security requirements and assesses risks in the available network and operational context. Companies and IT service providers receive traceable check results, technical evidence and AI-assisted remediation proposals. Changes remain under customer control and are made only after explicit approval.
Who is SigXOS for?
For companies with their own IT infrastructure and for IT service providers and system integrators who manage customer environments. The enterprise standard – secure, controllable, traceable and reliable to operate – applies to smaller companies too.
What does checking in context mean?
Whether a setting is appropriate depends on the role and configuration of the system in question. In the target architecture, SigXOS therefore takes system role, network environment and available dependencies into account and prioritises risks accordingly.
What role does AI play in SigXOS?
Checks are performed against defined security requirements. AI explains findings in plain language and prepares measures; it does not replace authorisation to execute. Local AI models in the customer network are planned. Approved external models are used only according to customer requirements and with controlled data sharing; credentials and keys stay outside the AI.
Does SigXOS replace an audit or a NIS-2 assessment?
No. Technical evidence supports audits and assessments but does not guarantee full regulatory compliance. Organisational measures, legal assessment and certification are outside its scope.
What is the current development status?
A working prototype for Cisco IOS/IOS-XE exists and has been tested with real devices and in simulation environments. The solution architecture describes the strategic target, not the scope that is fully available today. Further platforms and change functions will be added based on customer demand, market demand and technical validation.
Is SigXOS a fit for your environment?
You need to check and prove configurations regularly? Let’s find out in 30 minutes whether a pilot makes sense – directly for Cisco IOS/IOS-XE, for further technologies and platforms based on customer demand.