

Platform and solution architecture
SigXOS combines a dedicated SigXOS component per customer environment with a central platform operated in the EU/EEA and a customer portal for check results, approvals and evidence.
PrototypeStatus November 2026: working prototype for Cisco IOS/IOS-XE, tested with real devices and in simulation environments. The solution architecture describes the strategic target, not the scope that is fully available today.
Solution architecture
Strategic target architecture
Every customer environment gets its own SigXOS component, the SigXOS Edge. Credentials and raw configurations stay with the customer.
SigXOS
SigXOS customer portal
Results, technical review, approvals and documentation
- Check results and evidence
- Technical review and approvals
- Network and system overview: inventory, dependencies, operational relevance, customer requirements
- Tickets, reports and notifications
Customer contact & support
- Phone support
- Ticket system
- Approvals & coordination
- Onboarding & guidance
- Partner API & system integration
Per customer environment
SigXOS Edge
Local processing: collects configurations and inventory data read-only and runs the technical checks.
Customer systems
Network and security systems
Read and re-check · approved changes
- Customer A · networkOwn Edge processing · separate data, rights and orders
- Customer B · networkOwn Edge processing · separate data, rights and orders
- Customer C · private cloudOwn Edge processing · separate data, rights and orders
Same architecture pattern per customer
Central
Central SigXOS platform
Licences, versioned check packages and signed updates Operated in the EU/EEA
The API transfers check results, notifications and status to partner systems. Approving changes via partner systems is not part of the current target architecture.
Responsibilities and human control
Customer / commissioned service provider
Provide context, review measures and approve them within the authorised scope.
SigXOS
Develop the software, maintain and validate check packages, and provide technical controls for permissions, execution and evidence.
Process
Controlled check and change process
Checks · AI assistance · changes only after customer approval. Every step has a clear owner.
1Define scope
Define the check scope and access rights; capture systems and dependencies.
2Collect read-only
Collect configurations and inventory data strictly read-only.
3Assess in context
Assess configurations in the network and operational context, prioritise risks and propose measures.
4Review
Review measures, impact, tests and rollback procedures.
5Approve
Plan version, target systems and time window are approved by authorised customer owners or a service provider authorised to approve.
6Execute under control
Verify approval and prerequisites, back up the initial state and execute the approved plan.
7Verify and document
Check and document the result and operation. If required, start the prepared rollback procedure manually and check again.
- Deviation or missing approval: stop execution.
- No change order: close with a report and recommended actions.
- Implemented by the customer: SigXOS checks again and documents the result.
- Rework required: from review or approval back to step 3, no execution.
In the prototype and the pilot, the process ends with a report and recommended actions; you implement changes yourself and SigXOS checks again. Controlled execution of approved changes (steps 4 to 7) is part of the target architecture.
Development status
What the prototype does today
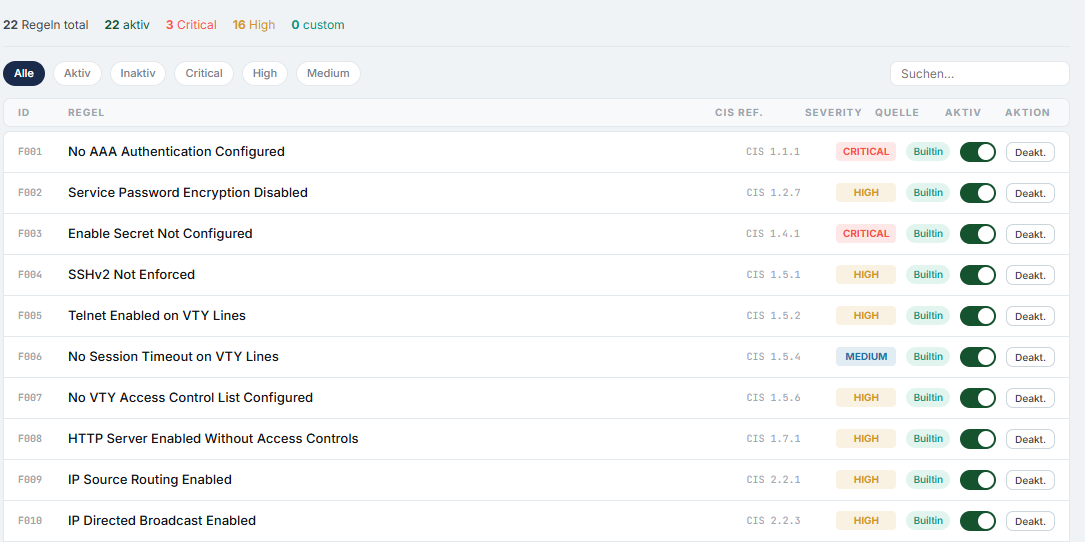
Working prototype for Cisco IOS and IOS-XE. Tested with real devices and in simulation environments.
Read-only collection
Collect configurations via SSH, without software on the devices.
CIS-oriented checks
Checks for Cisco IOS/IOS-XE with CIS reference and severity.
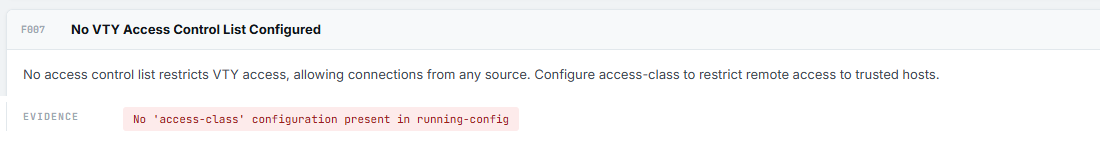
Findings with evidence
Every finding points to the configuration it refers to.
Inventory
Collected devices at a glance.
Audit trail
Check events and results documented in a traceable way.
Check report
Results of a check run as a report.
Inside the prototype
Original views from the prototype with lab data.

Technologies & platforms
Technologies & platforms
Today the prototype supports Cisco IOS and IOS-XE. The other entries are an example selection; platform support is extended based on customer demand, market demand and technical validation.
| Technology | Platform / check target | Status |
|---|---|---|
| Cisco | IOS / IOS-XE | Prototype |
| HPE Aruba Networking | AOS-CX | On customer demand |
| Fortinet | FortiOS | On customer demand |
| Palo Alto Networks | PAN-OS | On customer demand |
| HPE Juniper Networking | Junos OS | On customer demand |
| Linux | Red Hat Enterprise Linux, Ubuntu Server | Planned |
| Microsoft | Entra ID & Active Directory · check target: identity | Planned |
Naming a platform as an example does not mean it is already supported. Brands and logos are used solely for factual reference. Their use does not imply partnership, certification, approval or endorsement by the respective rights holders.
Security and privacy
Data and access control
For SigXOS, enterprise means secure, controllable, traceable and reliable operation in business environments – for smaller customers too.
Data stays with the customer
Credentials and raw configurations stay with the customer.
Controlled AI connection
Local AI models; external models only according to customer requirements, with a data filter before external transfer.
Separate customer environments
Own Edge processing; separate data, rights and orders.
Approval and evidence
Changes only after explicit approval; the execution service verifies the approval and limits changes.
Security functions in the target architecture: SSO/MFA · roles and permissions · secure credential management · encryption · logging · operational monitoring.
In the pilot: we agree on the operating location, data flows and any use of AI with you beforehand.
Licensing
Planned licensing model
Annual B2B software licences. Prices, package limits and pilot scope have not been finalised.
Companies
Annual licence per customer environment, tiered by the number of systems checked. Base package: security checks and technical evidence.
PlannedIT service providers and system integrators
Platform fee plus licence fees per managed customer environment.
Planned
Entry via a paid pilot. In addition: further check packages, customer-specific check requirements and onboarding and integration services.
Roadmap
Extended based on customer demand and validation
- Further technologies and platformsOn customer demand
- Linux and identity platformsPlanned
- Risk assessment in the network and operational contextPlanned
- AI-assisted remediation proposalsPlanned
- Controlled changes after customer approvalPlanned
- Mapping to further security requirementsPlanned
- Partner API & system integrationPlanned
- Partner modelPlanned
The first commercially available scope will be described bindingly in terms of supported platforms, versions, checks and operating limits. SigXOS does not claim full compliance with CIS, NIS-2, BSIG or other security requirements and replaces neither certification nor legal advice.
Is SigXOS a fit for your environment?
You need to check and prove configurations regularly? Let’s find out in 30 minutes whether a pilot makes sense – directly for Cisco IOS/IOS-XE, for further technologies and platforms based on customer demand.